SHA-256 Hashing vs Encryption: What Is Reversible?
SHA-256 hashing fingerprints data irreversibly; encryption scrambles it for later recovery. Learn the difference and when to use each.
What hashing does
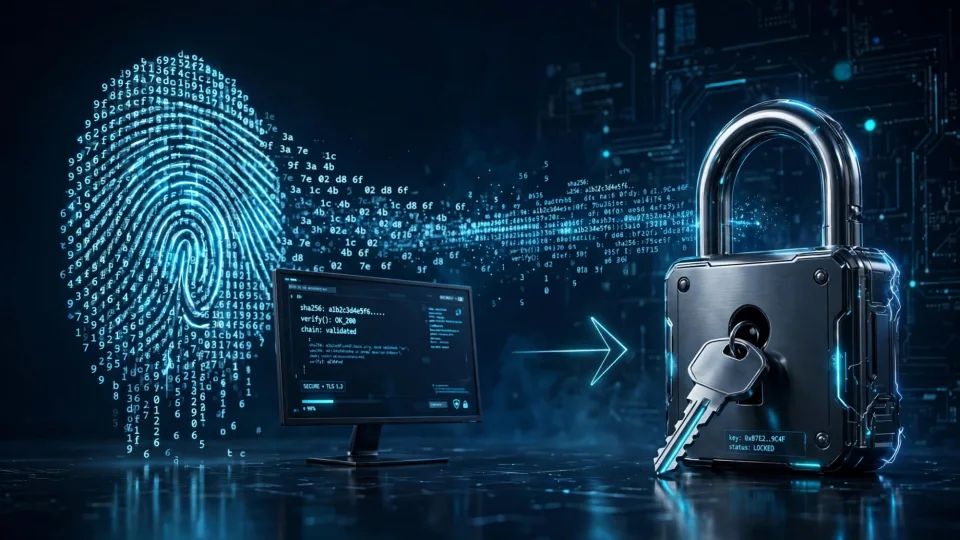
Imagine you want to prove a file has not changed since you last saw it, without keeping a second copy of it. A hash gives you a compact way to do that. Feed any amount of data into a hash function, and it returns a short, fixed-length fingerprint called a digest. The same input always produces the same digest, and even a tiny change to the input produces a completely different-looking digest.
SHA-256 is one of the most widely used hash functions. It belongs to the SHA-2 family, and its name states its output size: 256 bits, written as 64 hexadecimal characters. Whether you hash a single word or a whole book, the digest is always exactly that long. That fixed length is the first clue that hashing is not encryption: an encrypted message grows and shrinks with the message it protects, while a hash does not.
Hashing is also one-way by design. There is no key, and there is no "unhash" operation. Given only a SHA-256 digest, you cannot work backwards to the original text. The only general way to find a matching input is to guess inputs, hash each guess, and compare — easy for a common word, impractical for a long, random one. That asymmetry is the whole point: a digest can identify data without containing it.
Three properties make a cryptographic hash trustworthy here. It is deterministic: identical bytes always give the identical digest. It is preimage resistant: you cannot feasibly compute an input from its digest. And it is collision resistant in practice: finding two different inputs with the same digest should be infeasible. SHA-256 is the default in many systems because it has held up under years of scrutiny, while MD5 and SHA-1 have not and should no longer be used for security.
Hashing, however, proves neither secrecy nor origin: anyone can hash a guessable input and compare digests, and anyone can compute the same digest for data they created. If an attacker can change both a file and its published digest, the check still passes.
How encryption differs
Encryption solves a different problem: keeping data readable only to the people who should read it, while still allowing it to be read again later. Start with plaintext — the readable message — and transform it with an algorithm and a secret key into ciphertext, which looks like gibberish. Whoever holds the right key can reverse the process and recover the original exactly. Without the key, the ciphertext should stay unreadable.
The key is the crucial difference. Hashing has no key and no reversal; encryption is defined by its key and its reversal. Lose the key and you lose the data; leak the key and the protection is gone, even though the algorithm itself is public and well tested. Security lives in the key, not in keeping the method secret.
There are two broad families of encryption. In symmetric encryption, the same key encrypts and decrypts. AES is the standard symmetric algorithm, protecting everything from encrypted disks and backups to the web traffic behind the padlock in your browser. In asymmetric encryption, a public key encrypts and a separate private key decrypts, or vice versa for signatures. RSA and elliptic-curve algorithms work this way, typically exchanging a symmetric key securely at the start of a connection, after which the faster symmetric algorithm takes over.
Encryption also differs in shape. A ciphertext is roughly as long as the plaintext it protects, plus a small overhead in modern modes. Encrypt the same message twice with fresh randomness and you generally get two different ciphertexts, hiding whether two messages are identical. Hash the same message twice and you get the same digest both times — also a feature, but for a different purpose.
A useful mental model is the lock versus the fingerprint. Encryption is a lock: it guards a secret, and the key opens it again. Hashing is a fingerprint: it identifies something, but a fingerprint cannot be turned back into the person. Encoding, meanwhile, is neither: Base64, hex, and URL encoding merely rewrite bytes in a different alphabet, and anyone can decode them, with no key and no secret.
A worked example: hashing a harmless phrase
Let us make this concrete with a real hash. Using the FBSubNet SHA-2 Hash Generator, which runs entirely in your browser, I hashed the harmless demo phrase "hello fbsubnet" with SHA-256:
Input:  hello fbsubnet
SHA-256: 9253965a2c32eef0191c915f540bae9fd2fc4172eaa22bf4505e0be33f587a9f
Count it: 64 hexadecimal characters, exactly as promised. Now change just one character — add an exclamation mark — and hash again:
Input:  hello fbsubnet!
SHA-256: c1412d4e59dd94a4bd0aabe9a40cf75e7babcf131a4ab9cbd94ca9763fc288b5
The two digests look nothing alike, though the inputs differ by one character. This avalanche effect is why hashes spot tampering so well: flip one bit in a downloaded file and its digest changes completely, so a comparison against the publisher's digest fails loudly instead of silently passing.
The same phrase with the other SHA-2 sizes shows the fixed-length rule from the other side: SHA-384 gives a 96-character digest and SHA-512 a 128-character one, and both stay at those lengths however long the input grows:
hello fbsubnet
SHA-384: 94f76d94543b2ac596c6eeef8ed283fe5a739bcca8d9ffac0dd657e954d78dd6505e3c56ad95098257e42f93059daac7
SHA-512: f3a079671bd7c70d1c176b24037bfdd070279be138a37976abcd5a6a17f940112e607bc971b2b324a53d1a23c617d3a01b8e6647f3cfa5e817ae770ec708f27e
Now try the reverse. The tool offers no "decode" button, because there is nothing to decode. The only way back is to guess candidate phrases, hash them, and look for a match — quick for a short, guessable phrase, which is why password storage needs more than plain SHA-256, and unrealistic for a long, random input. That missing reverse operation is the definition of one-way.
For encryption, by contrast, nothing is lost in the round trip: the ciphertext holds the whole message, scrambled, and the key restores it. Where hashing keeps only a fingerprint, encryption preserves the message and guards it with a key.
Practical examples: when to use each
Use hashing when you need to verify, identify, or compare data without storing or revealing it. Download verification is the classic case: a publisher lists the SHA-256 digest of a release, you hash the file you downloaded, and matching digests mean the file arrived intact. Version control uses hashes to identify commits, and digital signatures sign a hash of a document rather than the whole document, keeping signatures compact while binding them to exact content.
Use encryption when you need to keep data confidential and read it again later. Full-disk encryption protects a stolen laptop, encrypted messaging protects conversations in transit and at rest, and encrypted backups let you store a copy off-site without trusting the provider with readable data.
Often you need both. A secure web connection encrypts traffic and uses hash-based authentication to detect tampering; a signed update is hashed for integrity and signed so you know who vouches for it. The two primitives answer different questions — "can only the right people read this?" versus "is this exactly what it claims to be?"
Password storage deserves special attention, because it is where the confusion causes the most damage. Passwords should be hashed, not encrypted: a login system never needs to recover your password, only to check your attempt by hashing it and comparing digests. But plain SHA-256 is the wrong tool here: it is fast, and fast is bad for password checking, because an attacker who steals the digest list can guess common passwords at great speed. Proper storage uses a deliberately slow, salted function — Argon2id, scrypt, or bcrypt — with a unique random salt per password, making mass guessing impractical. SHA-256 alone is not a password-storage scheme.
Side-by-side comparison
- Direction: encryption is two-way — decryption restores the message. Hashing is one-way — there is no decryption.
- Key: encryption needs a key, and the key is the secret. Hashing needs no key; anyone can compute the same digest.
- Output size: ciphertext grows with the message. A SHA-256 digest is always 64 hex characters, whatever the input size.
- Same input twice: modern encryption usually gives different ciphertext each time, thanks to fresh randomness. Hashing always gives the same digest.
- What it guarantees: encryption gives confidentiality — only key holders can read it. Hashing gives integrity and identity — this data is unchanged, and this is the data you mean.
- Typical uses: encryption for disks, messages, backups, and web traffic. Hashing for file verification, version control, digital signatures, and login checks.
Common mistakes to avoid
First, storing passwords with reversible encryption or fast unsalted hashing. If your system can decrypt a password, or an attacker can guess it quickly from its digest, the design is wrong. Use a dedicated password-hashing function with a unique salt per password, and never roll your own scheme.
Second, treating a hash as proof of origin. A digest tells you only that data matches a digest. If you downloaded both the file and its digest from the same compromised page, the check proves nothing. Trust comes from where the digest came from — a separate, authenticated channel or a verifiable signature. For messages between parties who share a secret, the keyed variant called HMAC adds authentication.
Third, assuming that hashing something makes it private. Hashing a phone number or email address does not anonymize it if the original values are guessable: anyone with a list of candidates can hash them all and match your "anonymized" records. Anything that must stay secret should be encrypted, or simply not collected.
Fourth, reaching for MD5 or SHA-1 out of habit. Both are broken for collision resistance: attackers have demonstrated ways to craft different inputs with the same digest. They linger in old systems, but no new security-sensitive work should rely on them. SHA-256 is the safe default. Finally, do not confuse any of this with encoding: if a value can be decoded by anyone with a standard tool, it was never protected.
Choosing the right tool, and trying it yourself
Start from the question you need answered. "May only certain people read this, and must they be able to read it again later?" — encrypt it, and guard the key as carefully as the data. "Is this the exact data I expect, unchanged?" — hash it, and get the expected digest from a source you trust separately from the data. "Did this person really send this?" — look to signatures, which combine hashing with asymmetric cryptography. "Should I store this credential?" — hash it with a slow, salted password function, never encrypt it, and never store it in readable form.
Open the FBSubNet SHA-2 Hash Generator and hash a phrase of your own. Change one character and compare the digests. Then sort your own problems into locks and fingerprints: a private journal needs encryption, a downloaded installer needs a hash check, and a password database needs salted slow hashing. Sorting those three cases correctly covers most of the mistakes in this article.
Frequently asked questions
Is SHA-256 encryption?
No. SHA-256 is a hashing algorithm, not an encryption algorithm. It produces a fixed-length, one-way digest with no key and no decryption step. Encryption is reversible with a key; hashing is not reversible at all.
Can a SHA-256 hash be decrypted?
There is no decryption operation for a hash. The only way to "reverse" one is to guess inputs, hash them, and compare — feasible for short or common inputs, impractical for long, random ones. That is why passwords need slow, salted hashing, not plain SHA-256.
Why is a hash always the same length?
That is the design of a hash function: it compresses any input into a fixed-size digest. SHA-256 always produces 256 bits, shown as 64 hexadecimal characters, whether the input is one word or an entire file.
Should I use hashing or encryption for passwords?
Hashing — specifically a slow, salted function such as Argon2id, scrypt, or bcrypt. Never store passwords encrypted, since anyone obtaining the key recovers every password, and never use plain SHA-256, which is too fast to resist guessing.