Base64 Encoding vs Encryption: The Difference Explained
Base64 looks like encryption, but it is not. Learn how Base64 encoding works, why anyone can decode it, and when to use real encryption instead.
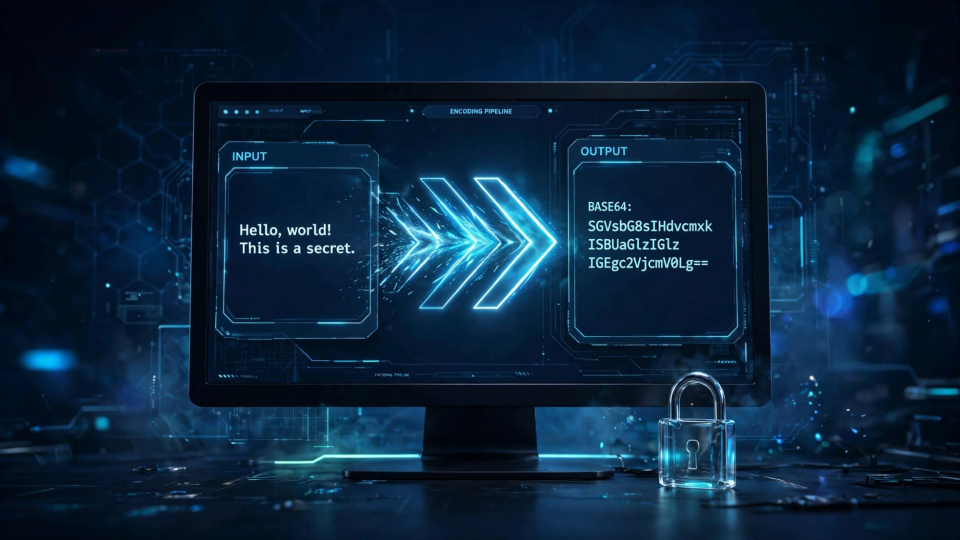
At first glance, Base64 looks like a secret code. Feed it a readable sentence and it hands back a jumble of letters, digits and equals signs that no human can read at sight. It is easy to conclude that the data has been protected — encrypted, even. It has not. Base64 is an encoding, not encryption, and confusing the two is one of the most common and consequential mistakes in everyday software work. This guide explains how Base64 actually works, proves with a worked example that anyone can reverse it in seconds, and shows what to use when you genuinely need secrecy.
How Base64 works
Base64 is a binary-to-text encoding scheme. Its job is to take arbitrary bytes — which may include values that text-based systems cannot carry safely — and represent them using only 64 safe, printable ASCII characters: A to Z, a to z, 0 to 9, and the two symbols + and /. That alphabet is public, fixed and standardised in RFC 4648.
The conversion works in groups. The encoder reads the input three bytes at a time — 24 bits — and splits those 24 bits into four groups of 6 bits. Each 6-bit group is a number between 0 and 63, and each number maps to one character in the alphabet. Three bytes in, four characters out, every time. That is also why Base64 output is roughly a third larger than the input: four characters now carry what three bytes used to.
Take the three letters "Man" as a concrete example. In ASCII, M is 77, a is 97 and n is 110, or in binary 01001101 01100001 01101110. Split into 6-bit groups you get 010011, 010110, 000101 and 101110, which are the decimal values 19, 22, 5 and 46. Look those up in the alphabet and you get T, W, F and u. So "Man" encodes to "TWFu" — arithmetic and a public lookup table, nothing secret.
Worked example: encode it, then decode it straight back
The fastest way to feel the difference between encoding and encryption is to do both directions yourself. Start with this plain sentence:
Hello, this is a test note.Run it through FBSubNet's free Base64 Text Encoder / Decoder and you get:
SGVsbG8sIHRoaXMgaXMgYSB0ZXN0IG5vdGUuNow paste that output into the same tool's Decode mode, or any other decoder. The result is the original sentence:
Hello, this is a test note.No password was asked for. No key was needed. No permission was checked. Anyone holding the encoded string can perform the same reversal in under a second. That single fact is the whole argument of this article: if reversal requires nothing you do not already have, the transformation cannot be protecting anything.
The padding rule is visible in smaller examples too. Encoding "Ma" gives "TWE=", because two bytes need one padding character; encoding just "M" gives "TQ==", because one byte needs two. Try both in the tool above and watch the trailing equals signs appear and disappear as you add or remove a character.
There is one more property worth noticing: Base64 is deterministic. The same input always produces the same output, everywhere, forever. Encryption is deliberately the opposite: encrypt the same message twice with a good modern cipher and you get different ciphertext each time, because a fresh random value is mixed in. Determinism suits a transport format but is fatal for secrecy, because it lets an attacker recognise repeated messages and build dictionaries of known encodings.
Why it is not encryption
Encryption and encoding solve different problems, and the difference comes down to one question: what does it take to reverse the transformation? With an encoding, the answer is "nothing but the algorithm", and the algorithm is public. With encryption, the answer is "the key", and the key is secret. That is the entire distinction, and everything else follows from it.
An encrypted message is unreadable to everyone except the holder of the key. A Base64 message is unreadable only to a human glancing at it — and only until that human pastes it into a decoder, which takes about three seconds. The scrambled appearance is a visual illusion, not a security property.
It helps to place Base64 alongside the two operations it is most often confused with:
- Base64 encoding changes how data looks so it can travel through text-only channels. It is reversible by anyone, needs no key, and protects against nothing except garbled transmission.
- Encryption changes who can read data. It is reversible only with the key, and its whole purpose is confidentiality — protecting data from eavesdroppers.
- Hashing, such as SHA-256, is one-way by design. It is not reversible at all, with or without a key, and its purpose is fingerprinting data or verifying a secret without storing it.
Real-world systems routinely combine these operations, which is part of why the confusion persists. A JSON Web Token, or JWT, is a good example: its header and payload sections are Base64URL-encoded, so they look scrambled — but anyone can decode them and read the claims inside. The security of a JWT lives entirely in its third section, the signature, which proves the token was issued by someone holding the signing key. The Base64 parts are packaging; the signature is the protection.
The classic cautionary tale is HTTP Basic Authentication. A username and password are joined with a colon and Base64-encoded into an Authorization header, producing something like dXNlcjpwYXNzd29yZA== for "user:password". Developers who assumed that string was encrypted shipped credentials in plain sight to every proxy, load balancer and log file that recorded the header. The encoding only exists so the credentials survive transport in a header field; any actual protection comes from TLS encrypting the whole connection underneath.
Appropriate uses: where Base64 genuinely shines
None of this means Base64 is useless — it is the right tool whenever the problem is format, not secrecy. Use it when data needs to survive a channel that only handles text.
Embedding small images in web pages is the textbook case. A data URI lets you place an image directly inside HTML or CSS, for example url('data:image/png;base64,iVBORw0KGgo...'), without a separate HTTP request. For tiny icons this saves a round trip; for larger images it backfires, because the roughly 33 percent size overhead and the loss of browser caching outweigh the benefit — link to a file instead.
Carrying binary data inside JSON APIs is another legitimate use. JSON only supports Unicode strings, so if an API must return a thumbnail, a signature or raw bytes, Base64-encoding them is the standard answer. Label the field, for example with an "encoding": "base64" property, so no consumer mistakes the payload for something else.
Email attachments work the same way: the MIME standard encodes attachment bytes as Base64 so mail infrastructure built for plain text can carry them unchanged. Pasting an encoded blob into a log or support ticket is likewise safer than pasting raw binary that a terminal or chat window might mangle.
Standard Base64 uses + and /, which clash with URL syntax — + reads as a space in query strings and / is a path separator. The URL-safe variant, Base64URL, swaps those two characters for - and _ and usually drops the padding. If your encoded value will appear in a URL, a filename or a token, use the URL-safe variant.
Mistakes that turn Base64 into a security hole
Most Base64 incidents are not exotic attacks. They are ordinary developers reaching for the nearest tool that makes data look unreadable, and stopping there. Watch for these patterns in code you write or review:
- Storing passwords as Base64. A Base64 password is a plain-text password with extra steps. The moment a database, config file or repository leaks, every credential falls in under a second. Passwords must be hashed with a slow, salted function such as bcrypt, scrypt or Argon2 — never stored in any reversible form.
- "Hiding" API keys or tokens in Base64. Encoding a key before committing it, logging it or sending it over an unencrypted channel protects it from nobody. Treat an encoded secret exactly as you would the raw secret, and rotate it immediately if it escapes.
- Encoding twice and calling it encryption. Running Base64 over Base64, or layering it with another trivial transformation, adds no secrecy. An attacker just decodes twice. Obscurity is not a layer of security.
- Assuming a JWT payload is private. Anything in a JWT's first two sections is readable by anyone who receives the token. Never put personal data or internal identifiers in token claims.
- Using standard Base64 inside URLs. A + that becomes a space or a / that splits a path corrupts the value in ways that are hard to debug. Switch to the URL-safe variant for anything that travels in a URL.
- Encoding text as bytes incorrectly. Base64 operates on bytes, not characters, so Unicode text must first be converted to bytes — UTF-8 is the standard choice. Skipping that step is how accented characters and emoji come back garbled after a round trip.
What to use instead, for each real need
When the requirement is genuine protection rather than transport, reach for the tool built for that job:
- Passwords: hash them with bcrypt, scrypt or Argon2id. These functions are deliberately slow and salted, so a leaked database still resists guessing, and they are one-way, so there is nothing to decode.
- Data in transit: use TLS. Encrypting the whole connection protects everything inside it, instead of relying on any single field looking scrambled.
- Data at rest: use a modern authenticated cipher such as AES-256-GCM or ChaCha20-Poly1305, with keys stored in a proper secret manager rather than in the code that uses them.
- Tokens and sessions: use signed tokens, where a cryptographic signature — not the encoding — proves authenticity, and keep sensitive claims out of the readable payload.
- Secrets in code and config: use environment variables or a secret manager. No encoding of a hard-coded secret makes it safe; the only fix is to stop hard-coding it.
A useful rule of thumb for code review: if the code that "protects" the data contains no key, no secret and no randomness, it is not protecting anything. Base64 has none of the three. If you can reverse the transformation without asking anyone for anything, so can an attacker.
For the credential side of this topic, FBSubNet's guide on passphrases vs passwords compares the two kinds of login secret and explains when each one is the right choice.
Frequently asked questions
Is Base64 secure?
No. Base64 provides no confidentiality, no integrity checking and no authentication. Anyone can decode it instantly with a browser console, a command-line tool or one of thousands of free online decoders. Never use it to protect passwords, API keys, personal data or anything sensitive.
Does Base64 compress data?
No — it does the opposite. Base64 output is roughly 33 percent larger than the input, because four characters now represent every three bytes. If you need both compression and text-safe encoding, compress first with gzip or a similar tool and then encode the compressed bytes.
Try it yourself
The quickest way to lock this in is a two-minute experiment. Open FBSubNet's Base64 Text Encoder / Decoder, type a sentence of your own, encode it, and then decode the result. Then try a string with an emoji or an accented character, and watch how UTF-8 handling keeps it intact. Each of those small observations is the theory above, visible in action — and none of them required a key.
The bottom line
Base64 changes how data looks; encryption changes who can read it. That one-sentence distinction decides whether a design is sound or silently exposed. Use Base64 freely for what it is for — moving binary data safely through text-only channels, embedding small assets, and debugging payloads. The moment the requirement becomes secrecy, reach for real cryptography: TLS for data in transit, AES-256-GCM or ChaCha20-Poly1305 for data at rest, and bcrypt, scrypt or Argon2id for passwords.